Financial Crime Intelligence
GhostCluster
AML FORENSICS & MULE NETWORK INTELLIGENCE SUITE
An institutional-grade forensic intelligence platform for detecting, tracing, and investigating complex money-laundering networks through transaction analysis, behavioral heuristics, network topology, evidence provenance, and AI-assisted compliance workflows.
Status note: GhostCluster is a research/engineering portfolio project run against synthetic and controlled demonstration data. It is not a deployed banking system, a FinCEN product, a law-enforcement system, or a certified compliance platform.
Project Overview
What is GhostCluster?
GhostCluster combines transaction-level analytics, entity intelligence, graph-based network analysis, heuristic detection, evidence management, and regulatory auditability into one investigative environment. Rather than flagging isolated suspicious transactions, it reconstructs the relationships between accounts, entities, and fund flows — surfacing the structure of a network so an analyst can decide what it means.
Every module is built around the same premise: an automated system can surface signal, but an investigator makes the determination. The platform is explicit about that boundary throughout — in its language, its workflows, and its audit trail.
Core Detection Engine
Multi-Dimensional AML Detection Engine
The platform evaluates transactions and entity relationships through multiple behavioral and structural signals. Every output below is a risk signal or investigative indicator — none of it independently proves criminal activity, and all of it requires analyst validation.
Sub-CTR Structuring Detection
Detects transaction clustering and repeated transactions designed to remain below applicable reporting thresholds.
Pass-Through Velocity
Identifies accounts receiving and rapidly sweeping funds while maintaining minimal residual balances.
Fan-In / Fan-Out Smurfing
Detects many-to-one and one-to-many transaction structures associated with coordinated fund movement.
Ghost Cluster Detection
Correlates account-level telemetry — device fingerprints, proxy IPs, user-agent overlaps — to identify potentially coordinated entities.
Round-Tripping & Cross-Border Sinks
Identifies circular transaction patterns and flows toward higher-risk jurisdictions or external liquidity destinations.
None of these signals, alone or combined, constitute a finding. GhostCluster surfaces structure — investigators determine meaning.
Investigation Workspace
Nine investigation modules, one case lifecycle.
Each module below is expandable — the workspace moves a case from first flag to regulatory-ready documentation.
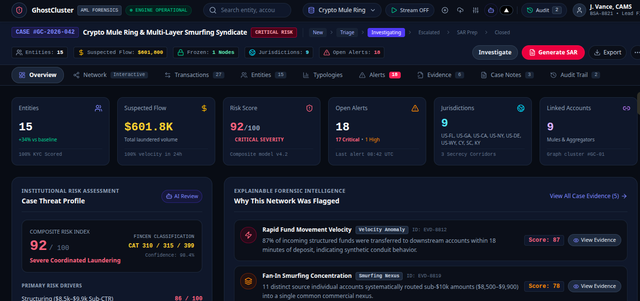
01Overview Dashboard
Live forensic KPIs
Overview Dashboard
Live forensic KPIs- Total monitored flow
- High-risk entities
- Structuring volume
- Quarantined accounts
- Average node velocity
- Open alerts
- "Why This Network Was Flagged" — evidence-backed risk drivers
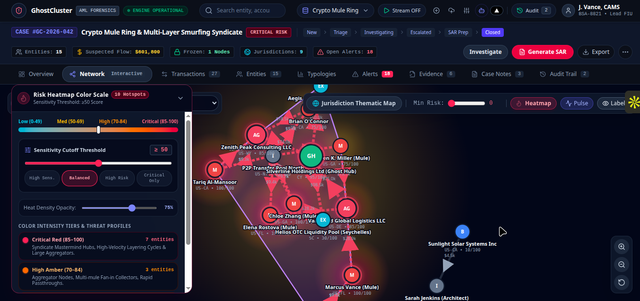
02Network Graph
Interactive force-directed graph
Network Graph
Interactive force-directed graph- Mule accounts, aggregators, pass-through entities
- Shell entities and network endpoints
- Transaction relationship edges
- Risk heatmaps & jurisdiction grouping
- Cluster isolation & node inspection
- Transaction-path highlighting
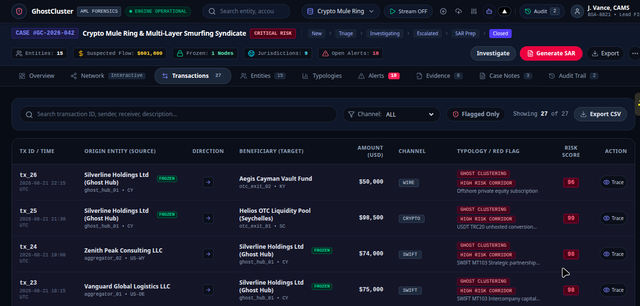
03Transaction Forensic Ledger
Search, filter, trace, export
Transaction Forensic Ledger
Search, filter, trace, export- Transaction search & account filtering
- Channel filtering — SWIFT, Fedwire, ACH, P2P, crypto
- Status filtering & structuring indicators
- Network tracing across linked accounts
- CSV export
04Entities & Mule Matrix
Risk-scored entity registry
Entities & Mule Matrix
Risk-scored entity registry- Risk score, account type, relationship count
- Inflow / outflow velocity, network exposure
- Account types — Consumer, Shell LLC, Crypto Exchange, Hub
Note: Administrative actions such as "Freeze Account" operate only against synthetic/demo data — this workspace is not connected to a real authorized banking system.
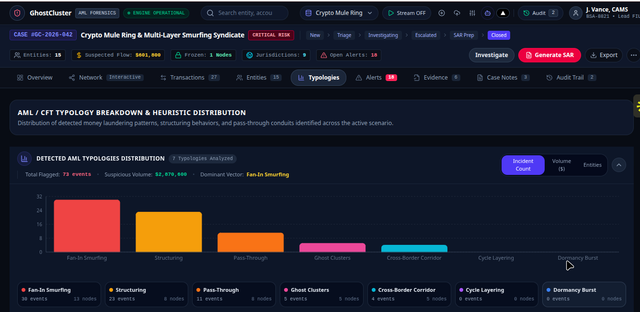
05Typology Analytics
Pattern & cluster dossiers
Typology Analytics
Pattern & cluster dossiers- Smurfing, rapid layering, structuring
- Crypto liquidation & pass-through behavior
- Cluster dossiers — estimated volume, node composition, primary channels
- Risk indicators & recommended investigative actions
06Live Alerts
Real-time triage stream
Live Alerts
Real-time triage stream- Critical · High · Medium severity tiers
- Review, Investigate, Escalate, Dismiss actions
Note: Alert actions in this portfolio build are simulated and do not trigger any real-world enforcement.
07Evidence Workspace
Provenance & chain-of-custody
Evidence Workspace
Provenance & chain-of-custody- Evidence records with verification timestamps
- Confidence scores per artifact
- SHA-256 hashes & source references
- Chain-of-custody metadata
08Case Notes Docket
Chronological investigation record
Case Notes Docket
Chronological investigation record- Note categories — Finding, Hypothesis, Regulatory Action, Evidence Log
- Investigator pinning
- Chronological case history
09Regulatory Audit Trail
Tamper-evident action log
Regulatory Audit Trail
Tamper-evident action log- Action, investigator, timestamp
- Previous hash / current hash chaining
- Regulatory reference per entry
Network Forensics
See the money. Understand the network.
Every case moves through the same investigative chain — from a single transaction to a filed narrative.
AI-Assisted Investigation
AI Investigation Copilot
The AI layer assists investigators — it does not replace them.
Important: AI-generated outputs are investigative assistance and require qualified human review before regulatory submission or operational action. The system does not independently determine criminality.
Reporting Workflow
AI-Assisted SAR Preparation
Structured around FinCEN SAR Form 111 and related BSA/AML regulatory context. The system assists with preparation — it does not automatically file reports.
Evidence & Provenance
Evidence you can audit.
Provenance is designed to support reproducibility, auditability, and investigator review — SHA-256 integrity hashes, timestamped records, source metadata, and chain-of-custody sequencing on every artifact.
Simulation Environment
Controlled Forensic Simulation
GhostCluster runs entirely on synthetic investigation scenarios — no real customer banking data is used anywhere in this build.
Metro Smurfing Ring
A coordinated fan-in structuring pattern across a metro-area account cluster.
Cross-Border Layering Corridor
Sequential transfers routed through intermediary jurisdictions before consolidation.
Shell LLC Aggregator Syndicate
Multiple shell entities feeding a single aggregator account.
All examples on this page are synthetic / demonstration data. GhostCluster does not have access to real customer banking data.
System Design
Technical Architecture
Request and data flow from ingestion through investigator-facing workspace.
Deployment
Deployment & Operational Design
Design Principles
Six principles behind the build.
Human-in-the-Loop
Analysts remain responsible for investigative conclusions and regulatory actions.
Evidence First
Every significant risk signal should be traceable to underlying evidence.
Explainable Risk
Risk scores should expose their contributing signals.
Auditability
Important actions should produce durable audit records.
Synthetic Testing
Detection logic should be testable without exposing real customer information.
Operational Restraint
Automated systems should assist investigators rather than independently impose enforcement decisions.
Portfolio Impact
Why I Built GhostCluster
Modern financial crime increasingly involves distributed accounts, rapid transaction chains, synthetic identities, cross-platform coordination, and complex networks — rather than isolated suspicious transactions.
GhostCluster explores how graph intelligence, behavioral heuristics, evidence provenance, and AI-assisted investigation can be combined into a unified forensic workflow. It's a research and engineering exercise in building investigative infrastructure that stays explainable and auditable as it scales — not a claim to have solved money laundering or to detect criminals automatically.
Key Takeaways
What the system is built around.
Transaction relationships become investigative context.
Risk indicators are linked to observable signals.
Investigative artifacts maintain provenance metadata.
AI supports investigators rather than replacing regulatory judgment.
Explore GhostCluster
Explore the Intelligence System
Walk through the detection engine, network graph, evidence workspace, and AI-assisted investigation workflow — running entirely on synthetic demonstration data.
GhostCluster is presented as a research/engineering portfolio project using synthetic or controlled demonstration data.